Reveal operational blind spots
Discover communicating assets and map their connections. Extend visibility across wired, wireless, endpoint and remote environments with the right sensors.
Nozomi Networks · AI-Powered OT, IoT & CPS Security
Nozomi Networks gives security and operations teams real-time visibility across OT, IoT and cyber-physical systems. Purpose-built monitoring, AI-powered analysis and OT threat intelligence help expose risk early while respecting the availability and safety requirements of critical operations.
Business outcomes
Discover communicating assets and map their connections. Extend visibility across wired, wireless, endpoint and remote environments with the right sensors.
Use passive network monitoring to gain deep OT and IoT visibility without generating additional traffic on critical control networks.
Baseline normal behaviour, then identify suspicious communications, malware, unwanted operations and unusual process values.
Combine vulnerability intelligence with asset criticality and operational context so teams can focus on practical risk reduction.
Centralise visibility, alerts and risk across plants, facilities and remote locations through cloud or on-premises management.
Track risk reduction with dashboards, benchmarks and audit-ready evidence for leadership, operations and assurance teams.
OT, IoT and CPS security
OT security operating cycle
Nozomi brings asset, network, vulnerability and threat context together so security and operations teams can make informed decisions without losing sight of safety and availability.
Continuously identify OT, IoT and cyber-physical assets across wired, wireless, endpoint and remote environments.
Map communications, protocols, roles, firmware, process variables and normal operational behaviour.
Connect vulnerabilities and exposures with asset criticality, operational impact and compensating controls.
Identify behavioural anomalies, malicious activity, suspicious communications and unusual process conditions.
Give IT and OT teams the evidence, workflow and remediation guidance needed to act safely and quickly.
Nozomi platform
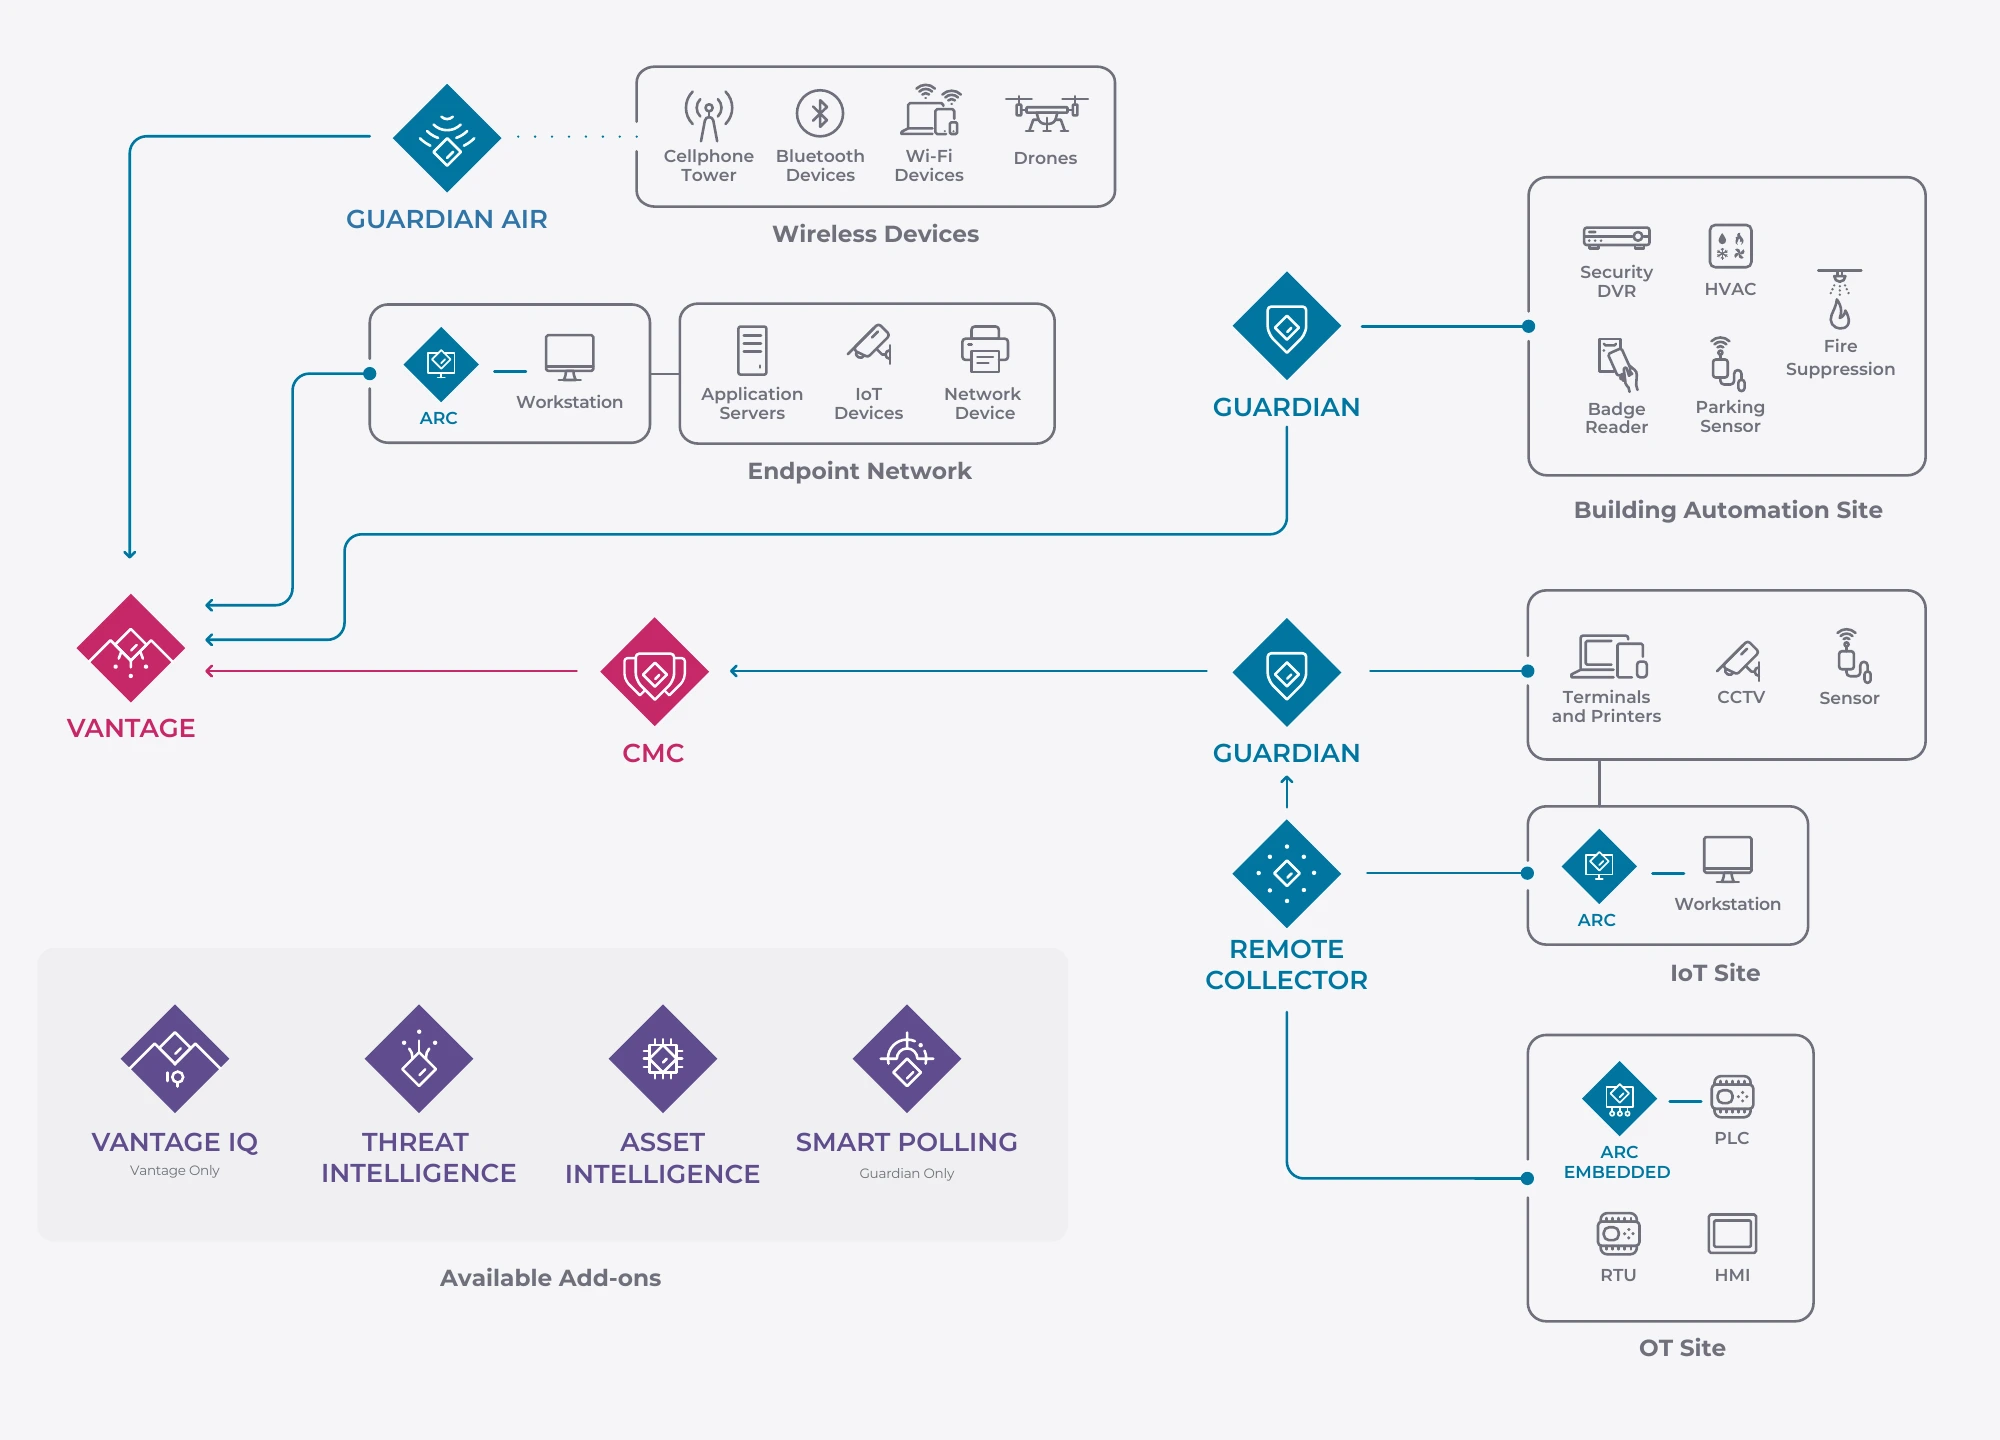
Choose a cloud or on-premises management model, then extend coverage with sensors suited to the operational environment.
Unify OT and IoT visibility, risk and security operations across sites through cloud-based Vantage or an on-premises Central Management Console.
Observe industrial network traffic without adding operational traffic, then build asset inventories, topology maps and behaviour baselines.
Extend asset and threat visibility to critical or isolated endpoints, including host activity, removable media and nearby network devices.
Monitor wireless frequencies used in operational environments and identify connected assets, rogue infrastructure and attack surfaces.
OT security capabilities
Build an inventory from observed communications, including device types, firmware and protocols. Optional Smart Polling adds approved active queries for deeper asset details.
See devices, zones, links, traffic patterns and dependencies to support segmentation and incident analysis.
Learn normal device, network and process behaviour to identify suspicious changes. Optional Vantage IQ adds AI-assisted alert correlation, risk prioritisation and natural-language investigation in the Vantage cloud platform.
Use indicators and research curated for OT and IoT environments to identify emerging threats and vulnerable assets.
Prioritise vulnerabilities and weaknesses using asset criticality, reachability, exploitability and operational context.
Bring alerts, asset details and process context together. Time Machine network-event replay helps teams examine the sequence around an incident and support root-cause analysis.
Connect operational telemetry and findings with existing SIEM, SOAR, ticketing and security workflows.
Use dashboards, benchmarks and audit-ready reporting to support programmes aligned with standards such as ISA/IEC 62443.
We plan monitoring around your critical processes, coordinate deployment with OT owners and establish a behaviour baseline. Alert tuning, agreed escalation paths and response ownership connect engineering, operations and security teams.
Build a picture of your observed assets and communications, understand priority risks and agree practical next steps. We scope the assessment around your sites and operational constraints.
OT security questions
It monitors assets, industrial communications, protocols, vulnerabilities, process behaviour and security events across operational technology, IoT and other cyber-physical systems.
Nozomi Guardian can passively observe mirrored network traffic or network taps without generating additional traffic on the monitored industrial network. The final architecture is reviewed against the site’s safety, availability and change-control requirements.
Guardian uses AI-powered analytics to baseline normal device, network and process behaviour and identify unusual activity. Optional Vantage IQ for the Vantage cloud platform adds alert correlation, risk prioritisation, remediation guidance and natural-language questions to support investigation.
Passive monitoring discovers devices communicating on the monitored network segments. Coverage depends on traffic and sensor placement. Optional Smart Polling uses approved active queries for deeper asset information; endpoint and wireless sensors can extend visibility where needed.
Nozomi can associate discovered assets with vulnerability and threat intelligence, then use operational context to support prioritisation. Remediation decisions still need to consider safety, vendor support and maintenance windows.
Yes. Guardian sensors and the Central Management Console support on-premises architectures, including environments with strict cloud connectivity or data-residency requirements. Deployment design depends on the required functions and network restrictions.
Yes. Vantage provides cloud-based central management across sites, while the Central Management Console supports centralised on-premises management. Sensors and collectors can be distributed according to the network architecture.
Nozomi supports integrations with common security, IT service management and response platforms. Apexagen confirms the required data flows, supported integrations and operating responsibilities during design.
Deployed to Deliver
Tell us about your sites, critical processes, existing monitoring and operational constraints. Apexagen will help define a practical visibility and security starting point.
Talk to an OT security specialist